

ACME.inc: The Ethical Calls a Pen Tester Makes Mid-Engagement
Day three of a pen test, you find a flaw that could give an attacker root. Do you keep going? A simulated engagement and the ethical calls a penetration tester makes along the way.
Articles, write-ups, and musings concerning the world of cybersecurity and technology.
Day three of a pen test, you find a flaw that could give an attacker root. Do you keep going? A simulated engagement and the ethical calls a penetration tester makes along the way.
Routine network enumeration turned up a shared folder full of plaintext employee passwords. Here's the memo that went up the chain — and the case for the free tool used to dig further.
Once you're inside a network, you're basically blind until you enumerate it. Enumeration builds a working picture of the hosts, services, and accounts actually present, so you can plan a next move instead of guessing one.
Once you have a target IP or domain, nmap can tell you a lot: the operating system, the services running and their versions, and which ports are open. Here's the quick version of how the OS-detection side works.
Cybersecurity professionals regularly face situations where what's legally allowed differs from what's ethically right. Understanding ethical frameworks helps you navigate these gaps and make decisions that protect both your organization and the public.
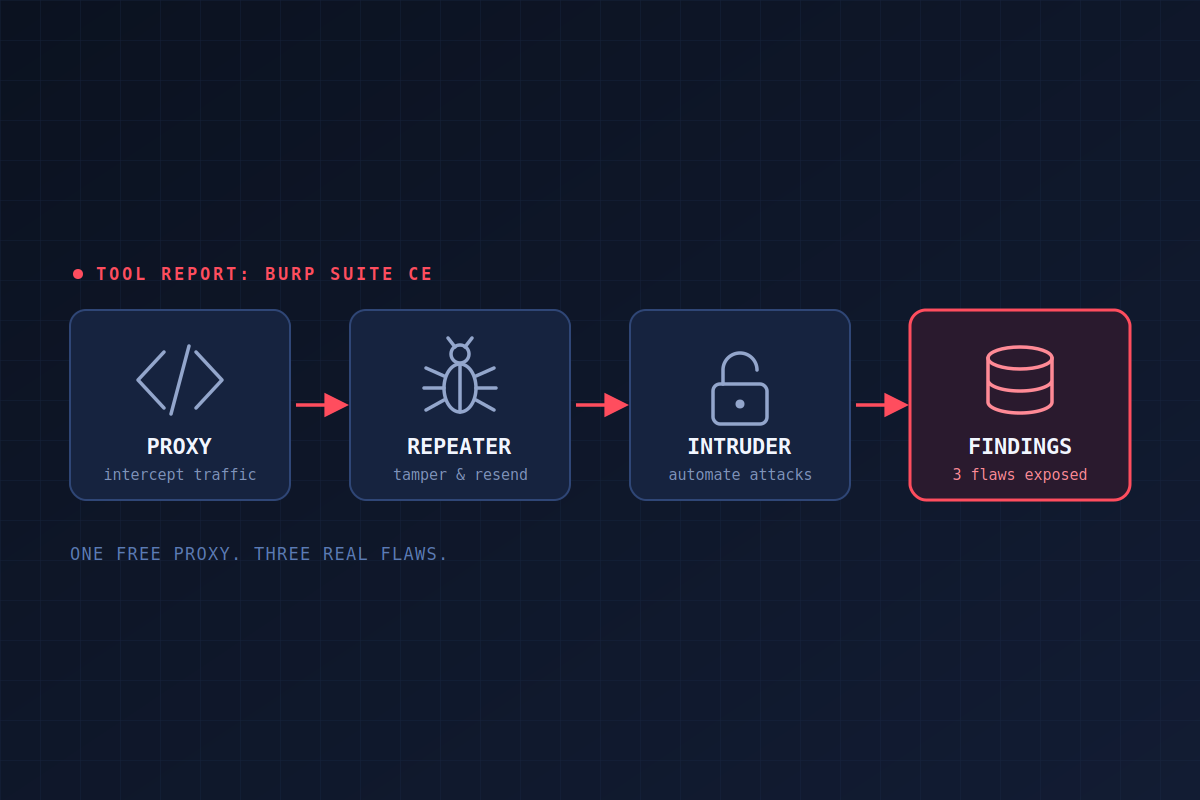
Three intentionally vulnerable apps, three classic web flaws, and one free tool that found all of them. Scope note: Everything here was done in a home lab, against deliberately vulnerable applications I run myself. Only test systems you own or have explicit written permission...
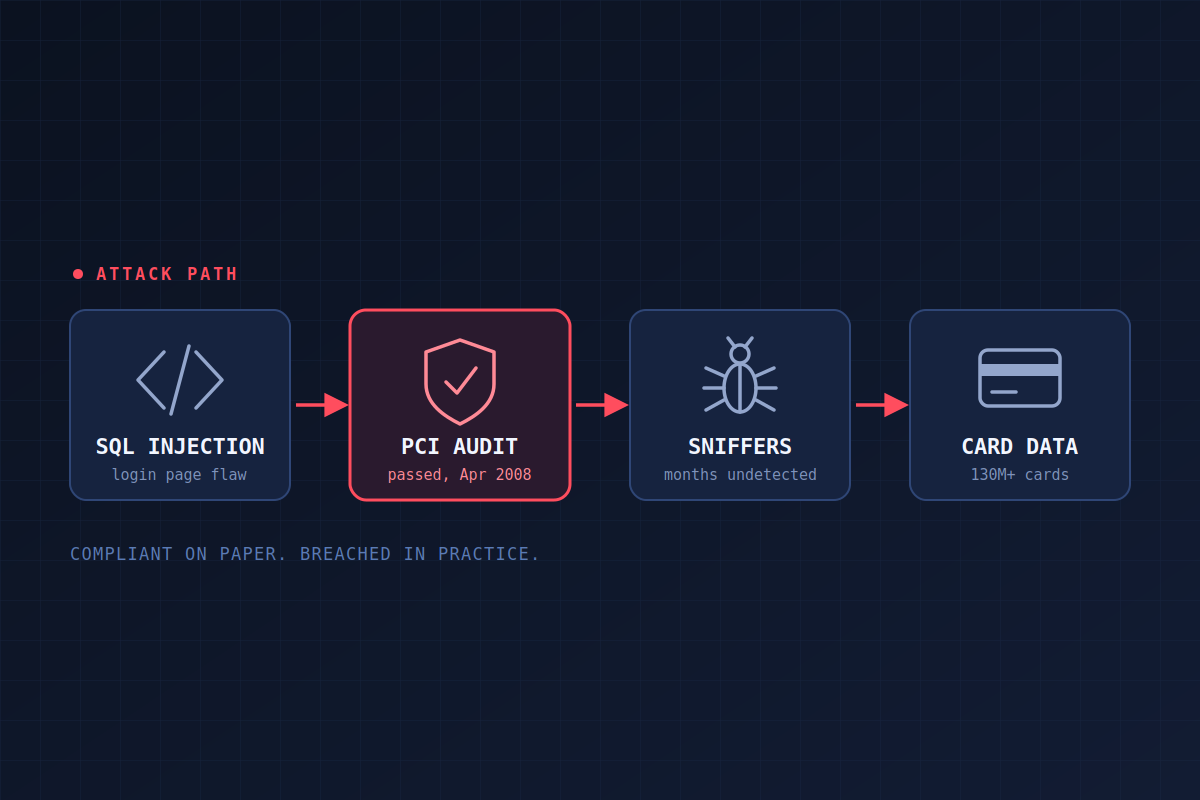
Heartland Payment Systems was PCI compliant while attackers were inside its network. When it disclosed the breach in January 2009, the theft was described as possibly the largest credit card crime in history. Based on public reporting and published analysis; sources are linked...